Private or on-premises
Dedicated entity or operation in its own infrastructure enables full data and operational sovereignty.
 VeriSeal©
Defense and Authorities
VeriSeal protects sensitive equipment, spare parts and documentation chains – with isolable operating models, strong roles and traceable security events.
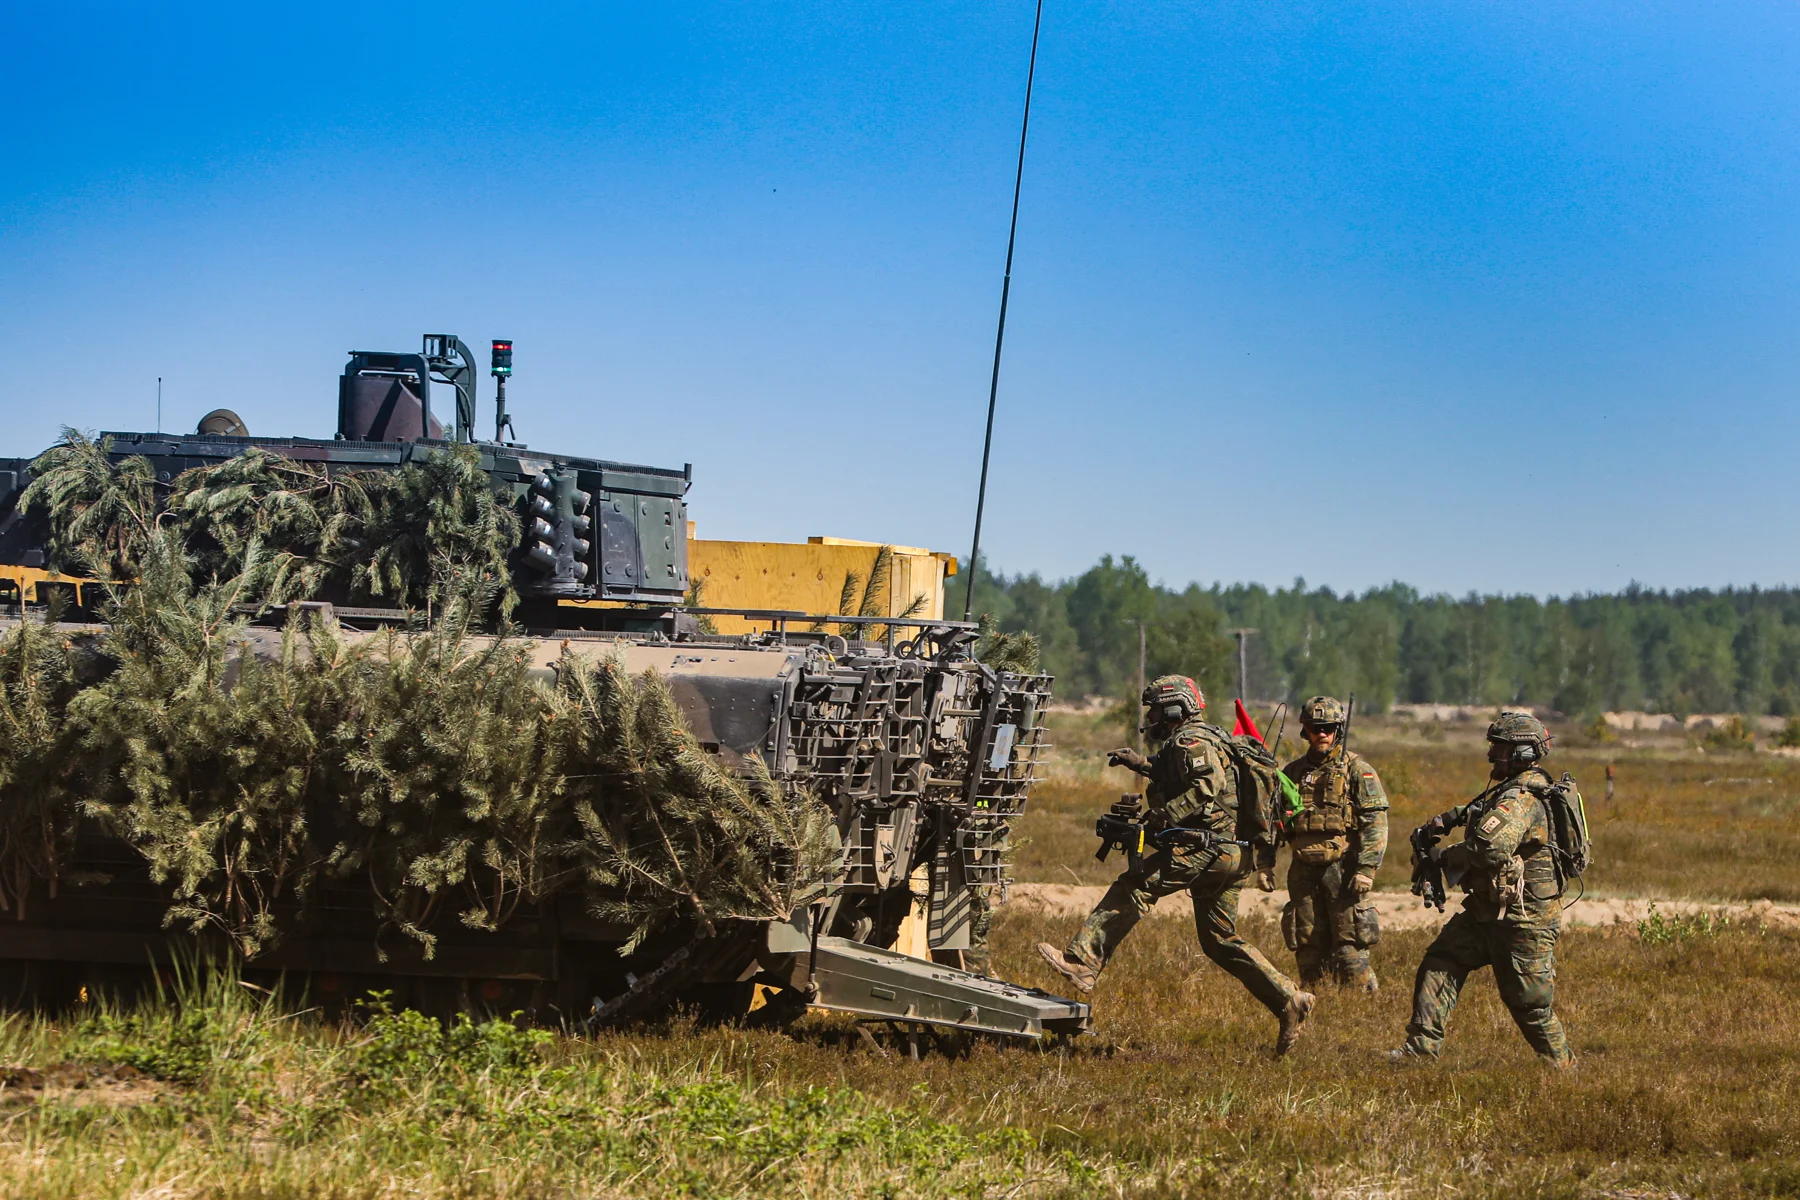
Bundeswehrsoldaten am Puma-Schützenpanzer · Oberlausitz, 16. Mai 2022. Staff Sgt. Gabriel Rivera-Villanueva / U.S. Army National Guard · Public Domain.
Historical photograph illustrating the audience, not a customer reference or endorsement by the Bundeswehr.
The appearance of U.S. Department of War (DoW) visual information does not imply or constitute DoW endorsement.
Initial position
Bei Materialübergaben müssen Gegenstand, Unterlagen und Zuständigkeit zusammenpassen. Fehlt eine Information oder ist eine Kennzeichnung auffällig, braucht es eine nachvollziehbare Klärung. Die digitale Unterstützung soll diese Zusammenhänge sichtbar machen, ohne sensible Angaben unkontrolliert weiterzugeben.
VeriSeal for your industry
Dedicated entity or operation in its own infrastructure enables full data and operational sovereignty.
Tamper loop, cryptographic status and server history combine physical and digital protection.
Clients, roles, MFA, mTLS and separate machine accesses reduce attack surfaces.
NFC, UHF, QR and barcode combine individual inspection, warehouse, transport and service.
This is how it works
Protection needs, operating model, roles and permitted data flows are defined.
Label and digital identity are assigned to a concrete object in a controlled manner.
Tests and state events generate a traceable safety profile.
Risk rules and interfaces transfer abnormalities to responsible systems.
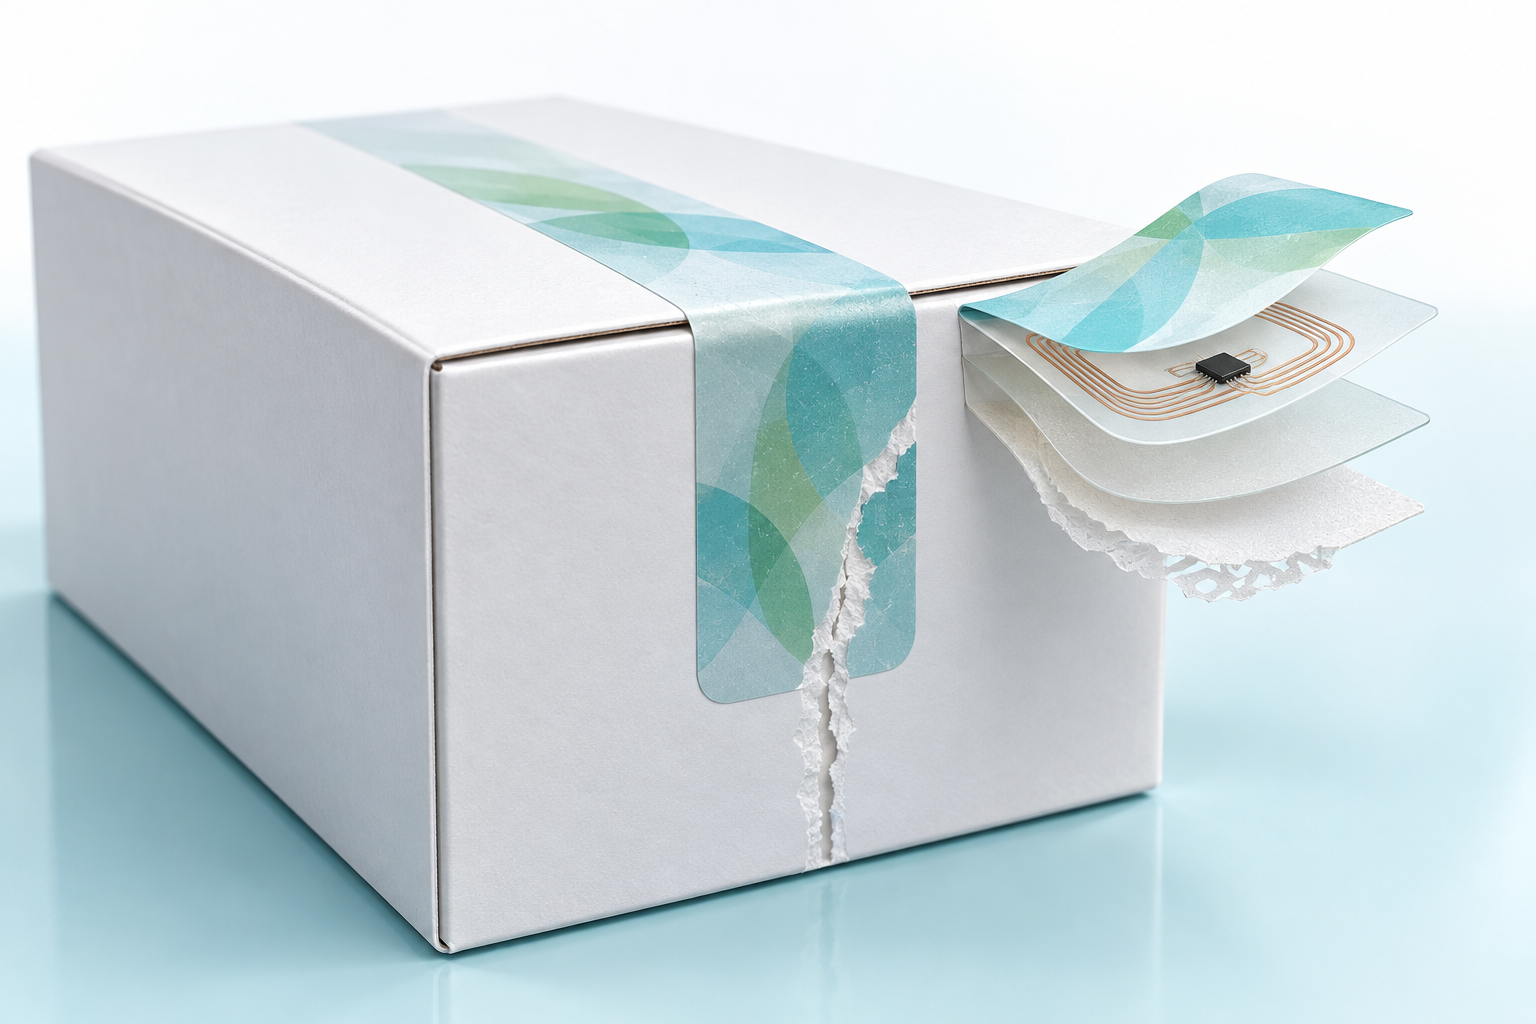 AI-assisted illustration · not a real customer installation
 Foto: Skot · CC BY-SA 4.0. Quelle und Lizenz Symbolfoto, keine VeriSeal-Kundenreferenz.
Simply explained
NFC, UHF, QR and serial number refer to the same controlled object.
Measurable in the pilot
VeriSeal is evaluated on the basis of real process indicators. Target values are derived together from the specific application.
Share of defined transfers, installations or maintenance with documented identity verification.
Time between detected safety event, evaluation and controlled response.
Conformity of physical object, UHF/NFC identity and leading inventory system.
Traceability of permitted roles, machine accesses and administrative changes.
Concrete operational cases
Component, origin, release status and technical documentation shall be checked before installation or maintenance.
Result: Reliable part identityA tamper-enabled label documents opening or damage to the box, device or protected area.
Result: visible manipulation statusUHF supports inventory and movement events; NFC enables targeted individual testing.
Result: combined mass and detail testingSecurity architecture
The test statement is derived from chip cryptography, product status, event history and controlled server logic. The UID remains a complementary feature.
NFC, UHF, QR and serial number refer to the same controlled object.
Cryptography, manipulation status, server release and history together form the test statement.
Private cloud or on-premise enables customer data management, key processes and network control.
Roles, MFA, mTLS, audit trails and defined transfers support safety operations.
Digital product identity
Ein Materialdatensatz kann Seriennummer und Kennzeichnung mit freigegebenen technischen Unterlagen, Versionsständen und dokumentierten Übergaben verbinden. Dabei wird unterschieden, welche Daten für Logistik, Instandhaltung oder Prüfung erforderlich sind. Ein hinterlegter Status ersetzt keine technische Abnahme oder Einsatzfreigabe.
Connection capability
Vorhandene Bestands-, Instandhaltungs- und Dokumentensysteme bleiben Teil der vorgesehenen Umgebung. Lesegeräte und vereinbarte Schnittstellen können Informationen dem richtigen Objekt zuordnen. Welche Kommunikation zulässig ist und wo Daten und Schlüssel verwaltet werden, muss vor einer Anbindung anhand der konkreten Infrastruktur festgelegt werden.
Classification
Für sensible Umgebungen werden Datenumfang, Berechtigungen und Betriebsgrenzen gesondert beurteilt. Offline-Verfahren benötigen eigene Regeln für Gültigkeit und späteren Abgleich. Aus einer allgemeinen Produktbeschreibung folgt keine Zulassung für Verschlusssachen, militärische Netze oder eine bestimmte Schutzklasse.
VeriSeal technically supports these processes. The specific validation, approval and regulatory evaluation is customer-specific.
A meaningful start
A delimited test combines real sample labels, real product data, system connection and a traceable testing process.
Ein Pilot verwendet ein abgegrenztes Materialbeispiel und ausdrücklich dafür freigegebene Daten. Gemeinsam werden eine Übergabe und eine anschließende Prüfung durchgespielt, einschließlich fehlender Nachweise oder gesperrter Kennzeichnungen. Der Test zeigt technische Möglichkeiten und Grenzen; eine weitergehende Verwendung setzt die zuständigen Sicherheits- und Betriebsfreigaben voraus.
Frequent questions
Yes. The on-premise edition is intended for operation on customer infrastructure; Specific network, key and operational requirements are defined in the project.
No. The label requires only minimal verification and identity data. Sensitive specialist data remains in the controlled system environment and is displayed depending on the role.
Offline scenarios can be provided, but their significance and synchronization depend on the need for protection. Online cryptographic verification provides the most up-to-date server decision.
The server-side status can be blocked or restricted. Events are logged and transferred to defined security or logistics processes.
Proof rather than assertion
VeriSeal can be operated without dependence on a shared Hawk-TEC database in an isolated private cloud or completely at the customer.
Pilot project
Label, process, interfaces and operating model in a structured initial consultation.